Security Readiness

Security Audits

Cloud, code, and compliance audits that find the risk hiding behind the checkbox.

Layered translucent planes revealing structure underneath, representing clarity and expert interpretation

The Open Security Experience

Where this service sits.

Discover → Validate → See & Act → Improve. This engagement lights the stages that match how Open Security delivers it — and stays connected to the rest of the experience.

  1. 01DiscoverSee where risk lives.
  2. 02ValidateProve what actually works.
  3. 03See & ActPrioritize and close it.
  4. 04ImproveGet stronger next cycle.

The problem

Compliant and secure are not the same thing.

Frameworks like PCI, HIPAA, and SOC 2 set a floor, not a defense. Audits that stop at evidence collection leave cloud misconfigurations, IAM sprawl, and code-level risk untouched.

  • Breached companies pass audits every year — the binder was never the path.

  • Cloud and IAM findings live in a compliance tracker, separate from what security is actually closing.

  • The report maps controls to a framework and never asks whether those controls reduce attacker success.
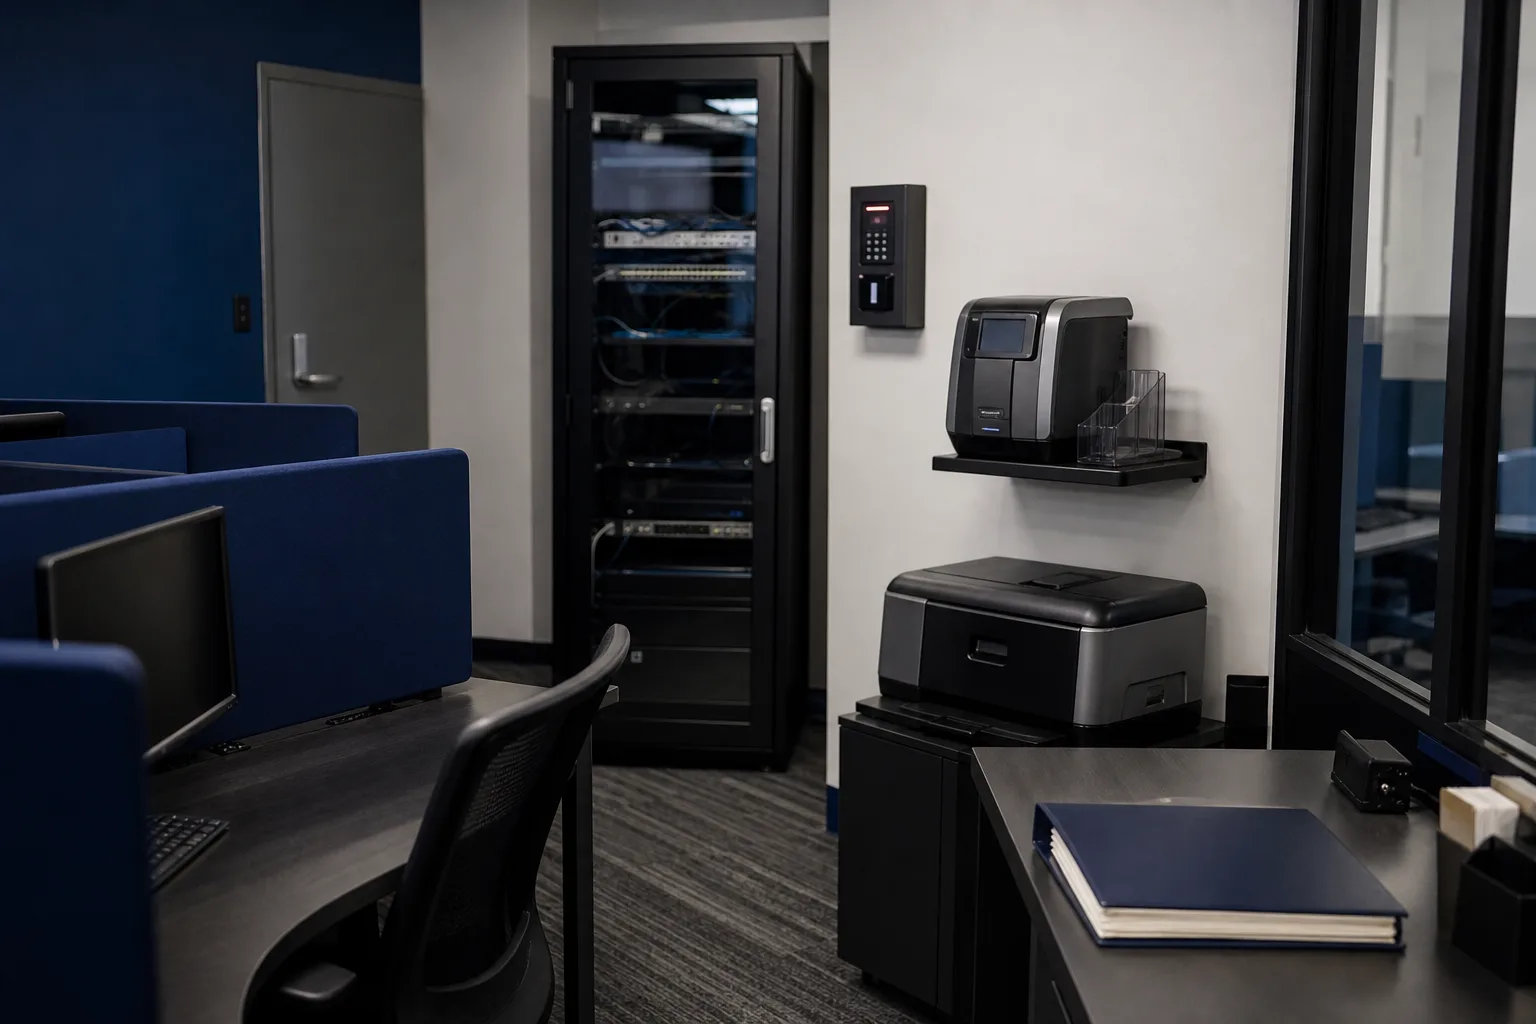
Control and architecture view used to distinguish compliance evidence from attacker-valuable gaps

How the engagement is run

The work, from context to follow-through.

Operators run the engagement. You stay in the decisions that shape scope, evidence, and what gets closed.

What's in scope

  • Cloud control plane and IAM review
  • Code and secrets hygiene sampling
  • Compliance mapping (PCI, HIPAA, SOC 2)
  • Third-party integration risk review

The relationship

A program, not a one-day exercise.

An audit that ends at the evidence pack is a moment. Connecting those gaps to the rest of your exposure — and to the fixes you will still be working next quarter — is how compliance stops living in a silo.

  1. 01

    Findings split into quick wins and strategic fixes so work starts before the binder is finished.

  2. 02

    Technical gaps can register with the rest of your exposure instead of a separate compliance tracker.

  3. 03

    The next cycle measures whether last audit’s closures still hold — not whether you can collect the same screenshots again.

The Open Security difference

We audit like attackers read the report.

  1. 01

    Control gaps tested for real attacker value, not just framework mapping.

  2. 02

    Cloud control plane, IAM, and secrets hygiene reviewed by operators who exploit these gaps elsewhere.

  3. 03

    Findings split into quick wins and strategic fixes so progress starts immediately.

Outcomes

What is different when you leave.

  1. 01

    A control-gap matrix tied to PCI, HIPAA, and SOC 2

  2. 02

    An evidence pack ready for auditors and boards

  3. 03

    A quick-win vs. strategic-fix roadmap

  4. 04

    Confidence that compliance maps to actual protection

Related technology

Operators do the work. Technology keeps it connected.

Portal

How Portal keeps audit work in the program view

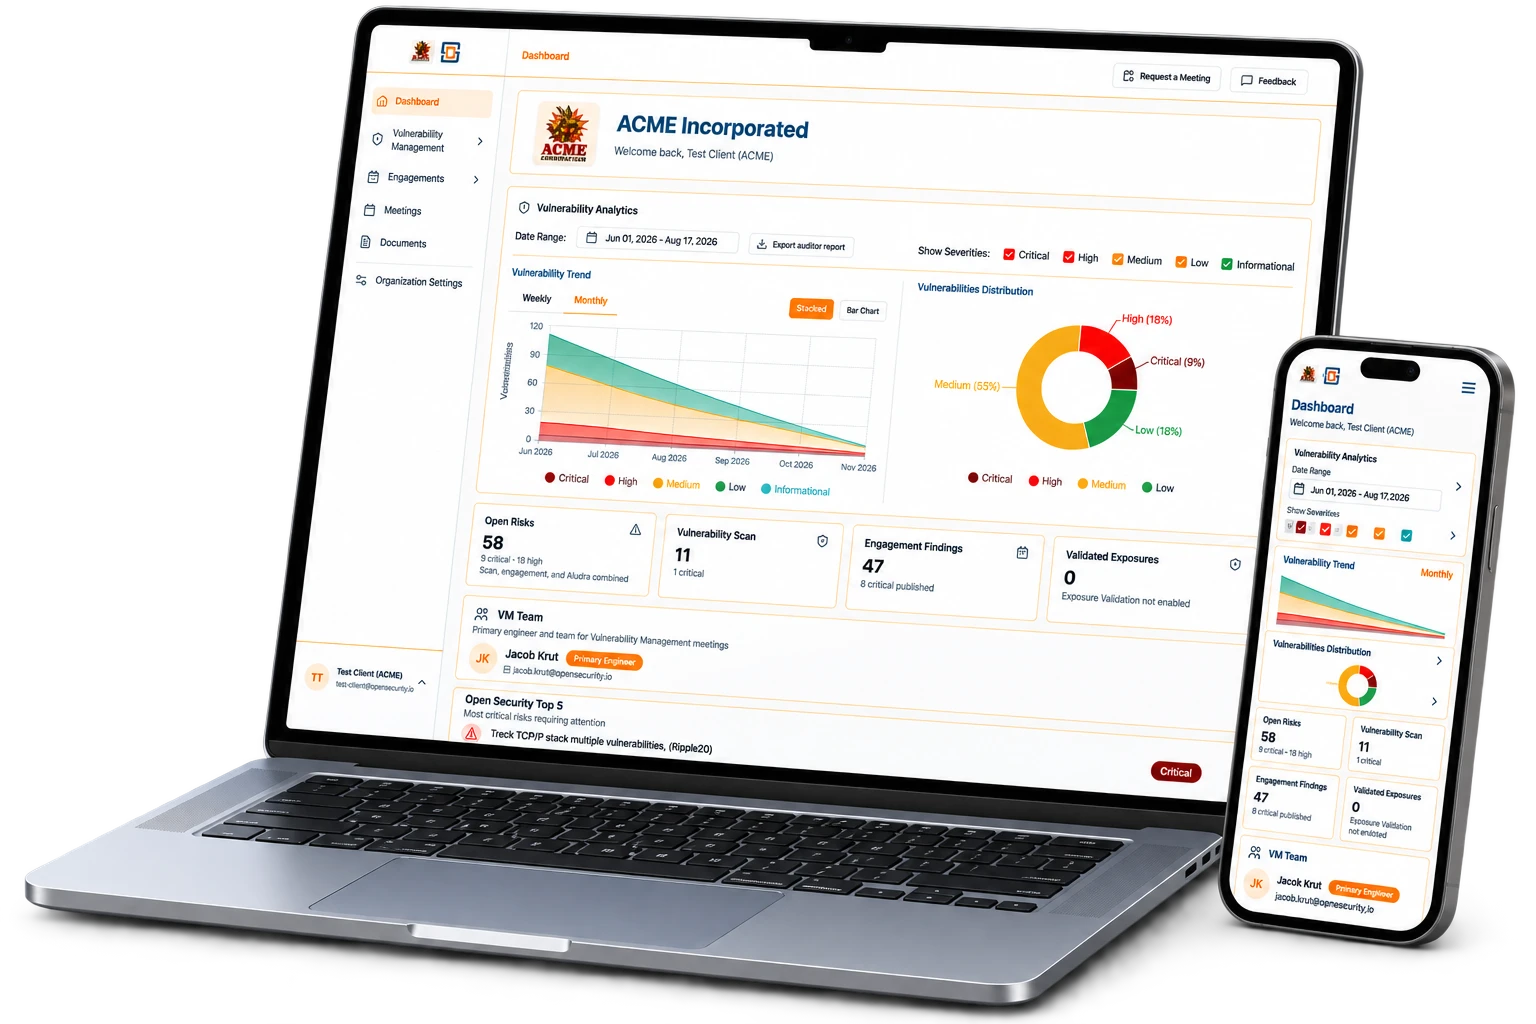
Evidence, remediation status, and the next close can sit in Portal with the rest of the engagement — so the board is not assembling a compliance story by hand.

Explore Portal →
Open Security Portal shown as the client view for engagement and audit reporting

Sirius

How Sirius keeps audit fixes beside exposure

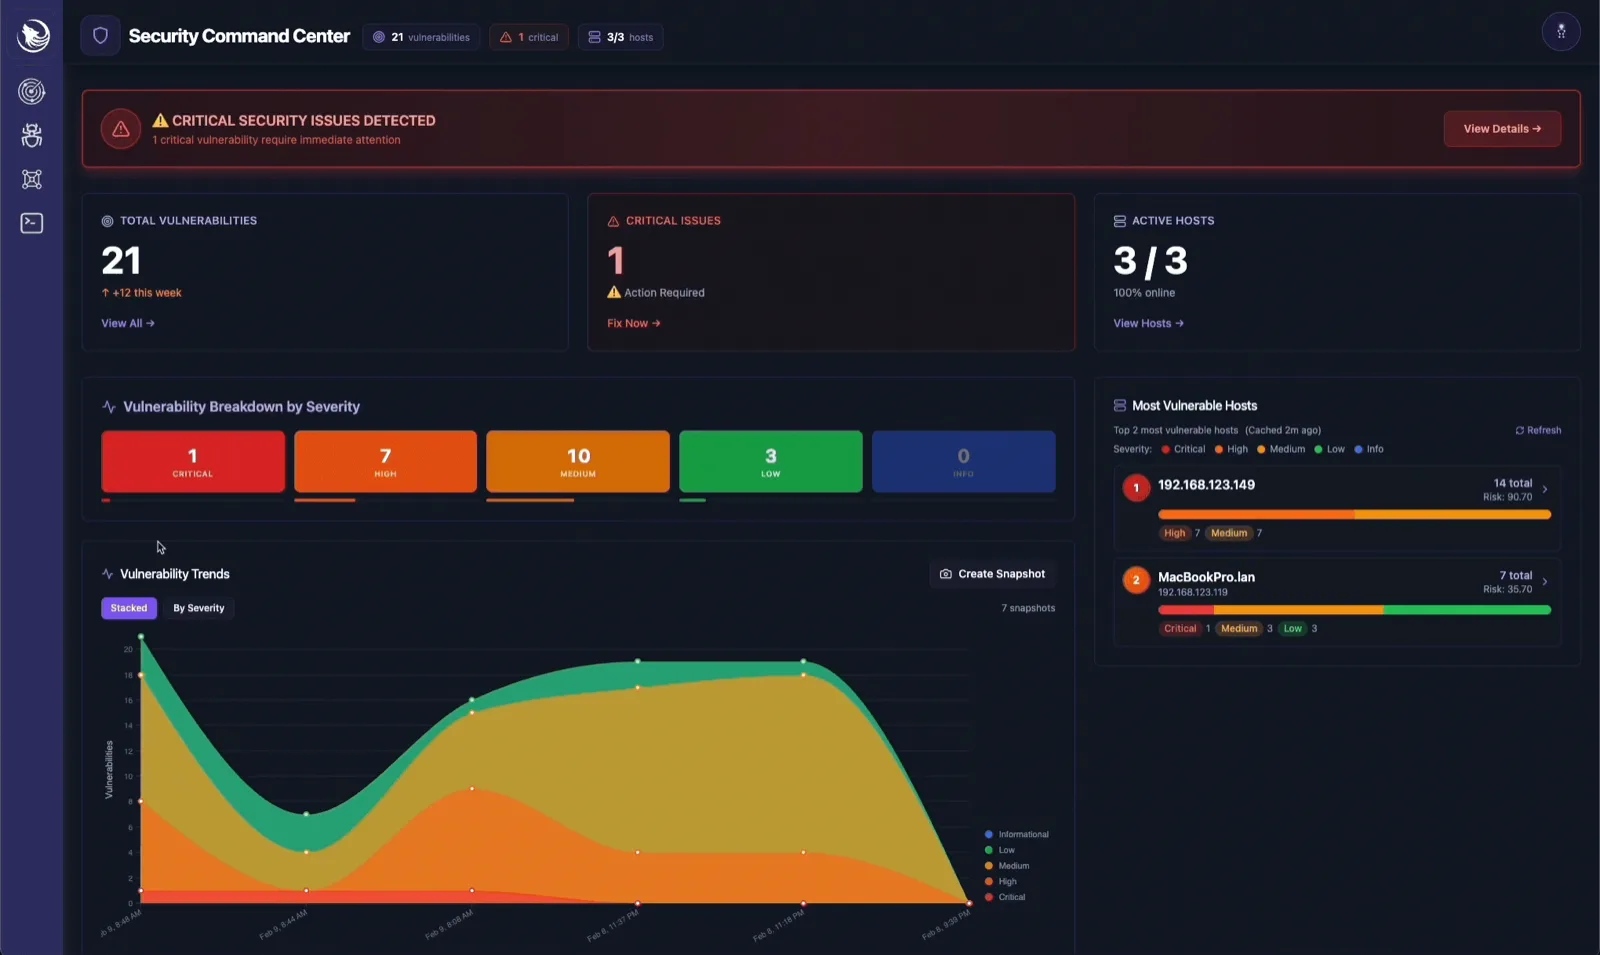
Technical audit findings register in Sirius with the rest of your exposure, so audit remediation is prioritized alongside vulnerabilities instead of living in a silo.

Explore Sirius →
Sirius dashboard where audit remediation sits with the rest of exposure

Common questions

Is this a checkbox audit?

No. We map to the frameworks you answer to, then test whether those controls actually reduce attacker success.

Which frameworks do you cover?

PCI, HIPAA, and SOC 2 are the common set. We confirm the standard — and the parts of the environment that matter — in scoping.

Will this replace our external auditor?

No. We find the risk hiding behind the checkbox and pack evidence your auditor and board can use. We do not issue the attestation.

How technical is the work?

Cloud control plane, IAM, secrets, and code sampling are in scope. Operators who exploit these gaps elsewhere review them here.

What happens to findings after the audit?

They can register in Sirius with the rest of your exposure so audit remediation is prioritized alongside vulnerabilities — not lost in a separate tracker.

The Open Security Experience

What comes before and after.

You do not need to buy the entire platform. These stages show how this service becomes more powerful as part of the Open Security Experience.

Find the risk hiding behind the checkbox.

Talk with an operator about the standard you answer to — and whether the controls behind it actually reduce attacker success.