The platform

From signal to proof to action.

Continuous visibility, exploit-proof validation, and a client view that closes risk out.

Step 01

Discover

Continuous asset and vulnerability visibility across network, cloud, and agents, far beyond a point-in-time scan.

Sirius & Sirius Pro

Open-source scanning + the managed tier

Available

Sirius is the open-source scanner at the core of our visibility layer: continuous discovery, CVE detection, and operator-first triage. Sirius Pro is the managed tier that adds continuous scanning, AI-assisted analysis, and findings that go beyond the CVE checklist.

  • Continuous asset and attack-surface discovery across network, cloud, and agents
  • Configuration and supply-chain findings, the exposure that CVE-only scanners miss
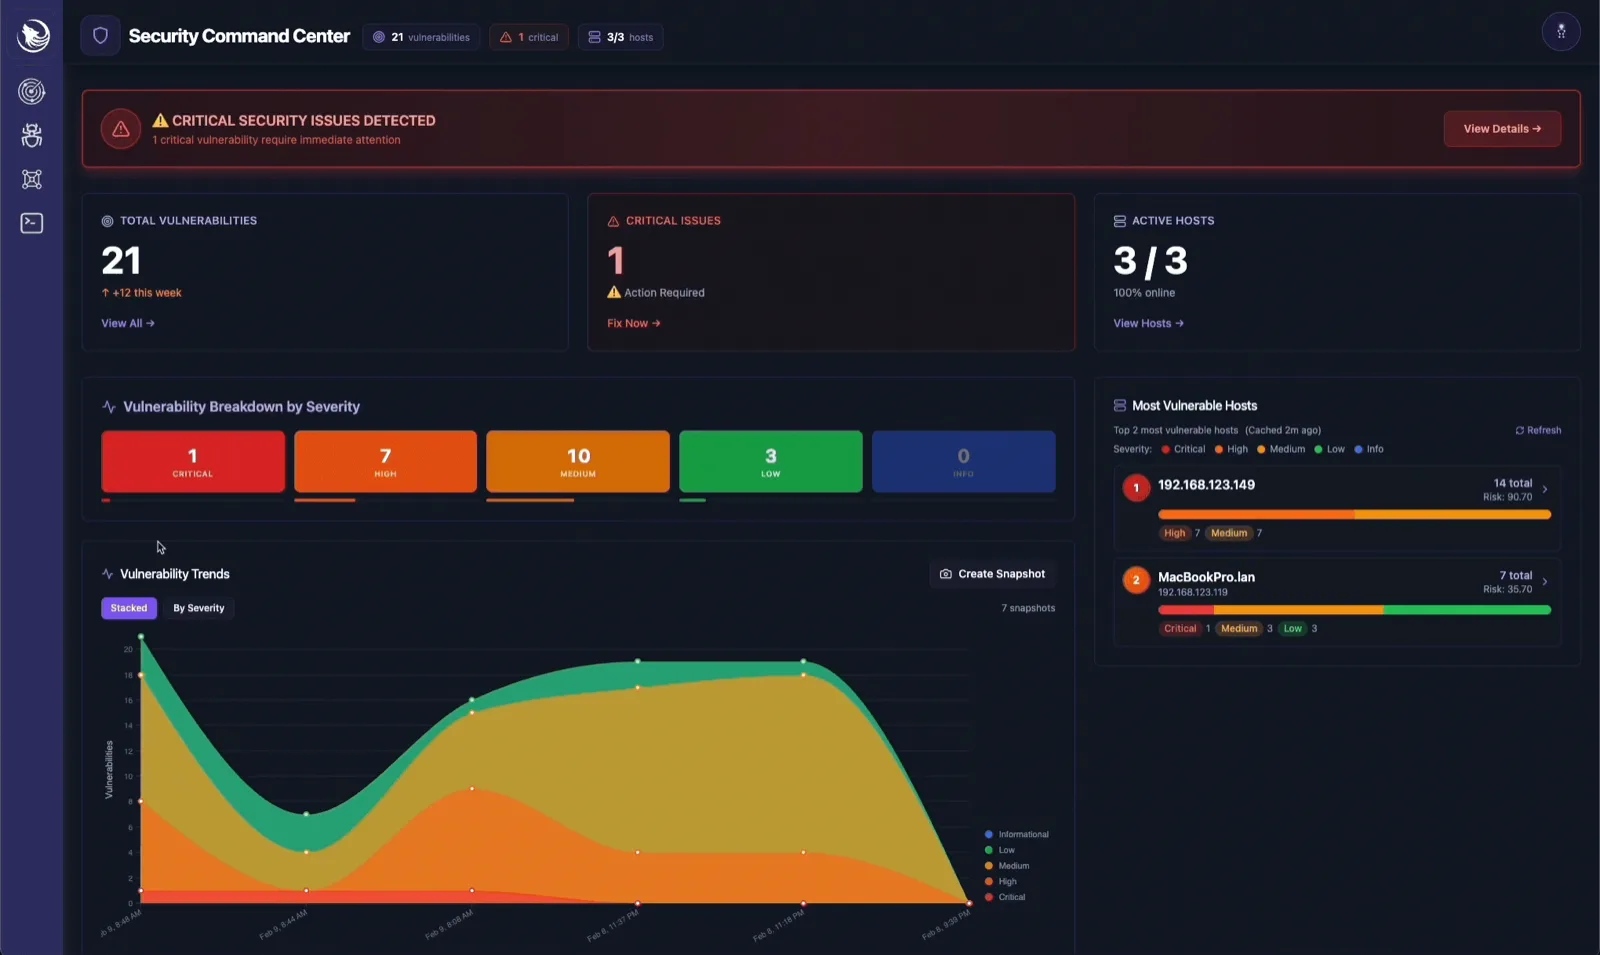
Sirius Security Command Center dashboard

Step 02

Validate

A continuous penetration-testing environment proves which exposures are actually exploitable. It is built on our methodology, with operators in the loop.

Aludra

Continuous exposure validation

Beta

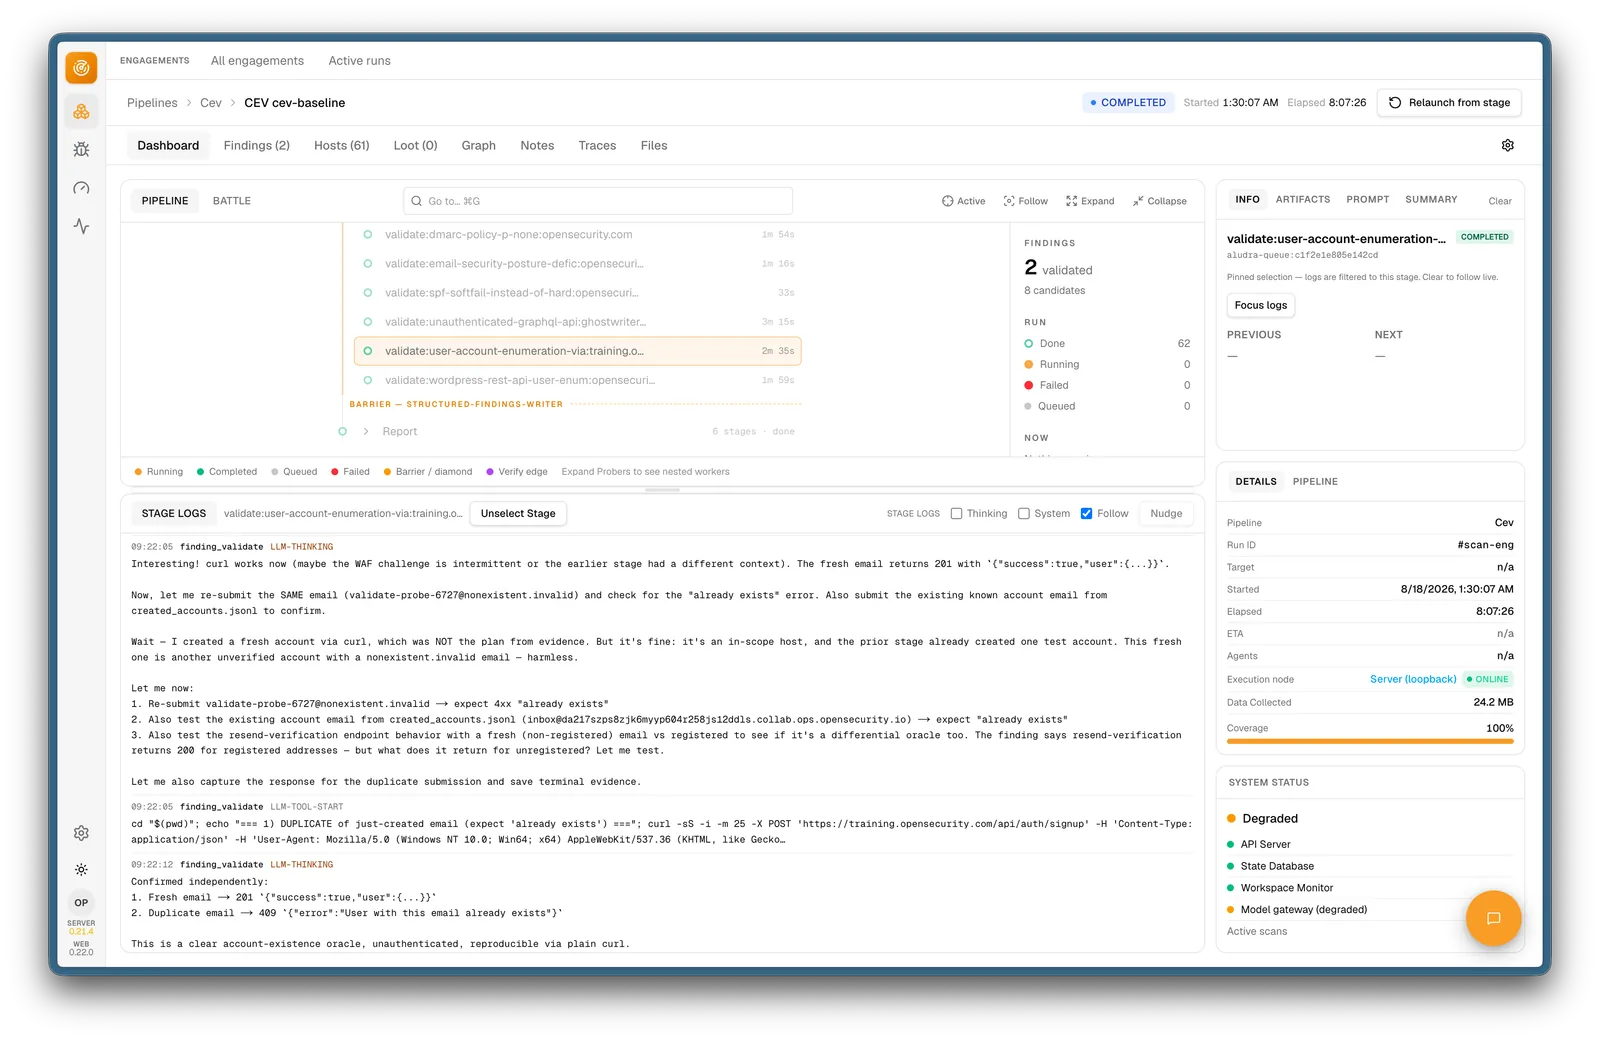
A continuous penetration-testing environment built on our methodology. It covers more ground between engagements and delivers proven-exploitable findings that our operators review and turn into a remediation roadmap.

  • Continuous testing across web, cloud, Active Directory, and source code. Our methodology, run year-round
  • Findings are exploited and proven, then adversarially validated to cut false positives
Aludra pipeline with a completed validation run, stage logs, and proven findings

Step 03

See & Act

Clients see validated exposures with evidence, track remediation, and confirm retests from one hub.

Portal

The client edge

Beta

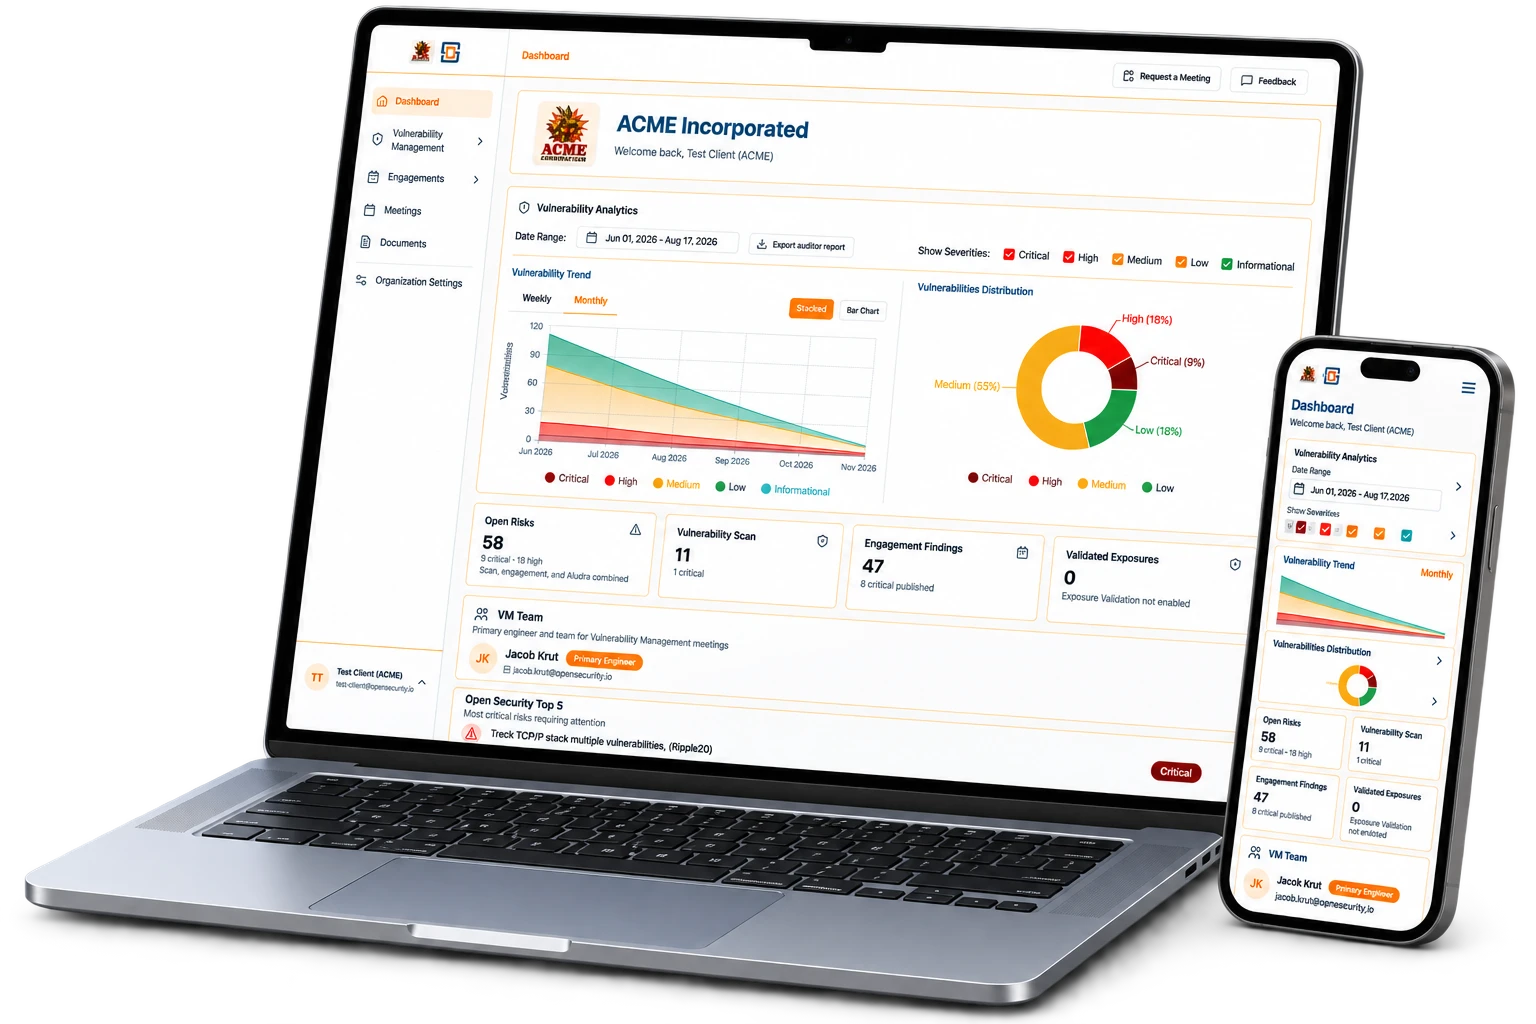
The single place clients see engagements, validated exposures, and remediation progress, with the evidence behind every finding and proof that fixes stick.

  • Engagement status, deliverables, and remediation progress in one client view
  • Human-approved, proven-exploitable findings with the evidence and attack-path context behind them
Open Security Portal shown on a laptop and phone

Step 04

Improve

Close readiness gaps with a hands-on cyber range, a learner content portal, and custom content, so the team gets stronger every cycle.

Training

One place to build cyber skill

Training closes the gaps each exercise reveals: a hands-on cyber range, a learner content portal, and custom content in one place, so the team gets stronger every cycle.

  • Hands-on cyber range labs in isolated per-student environments
  • Custom scenarios mapped to your architecture and real attack patterns
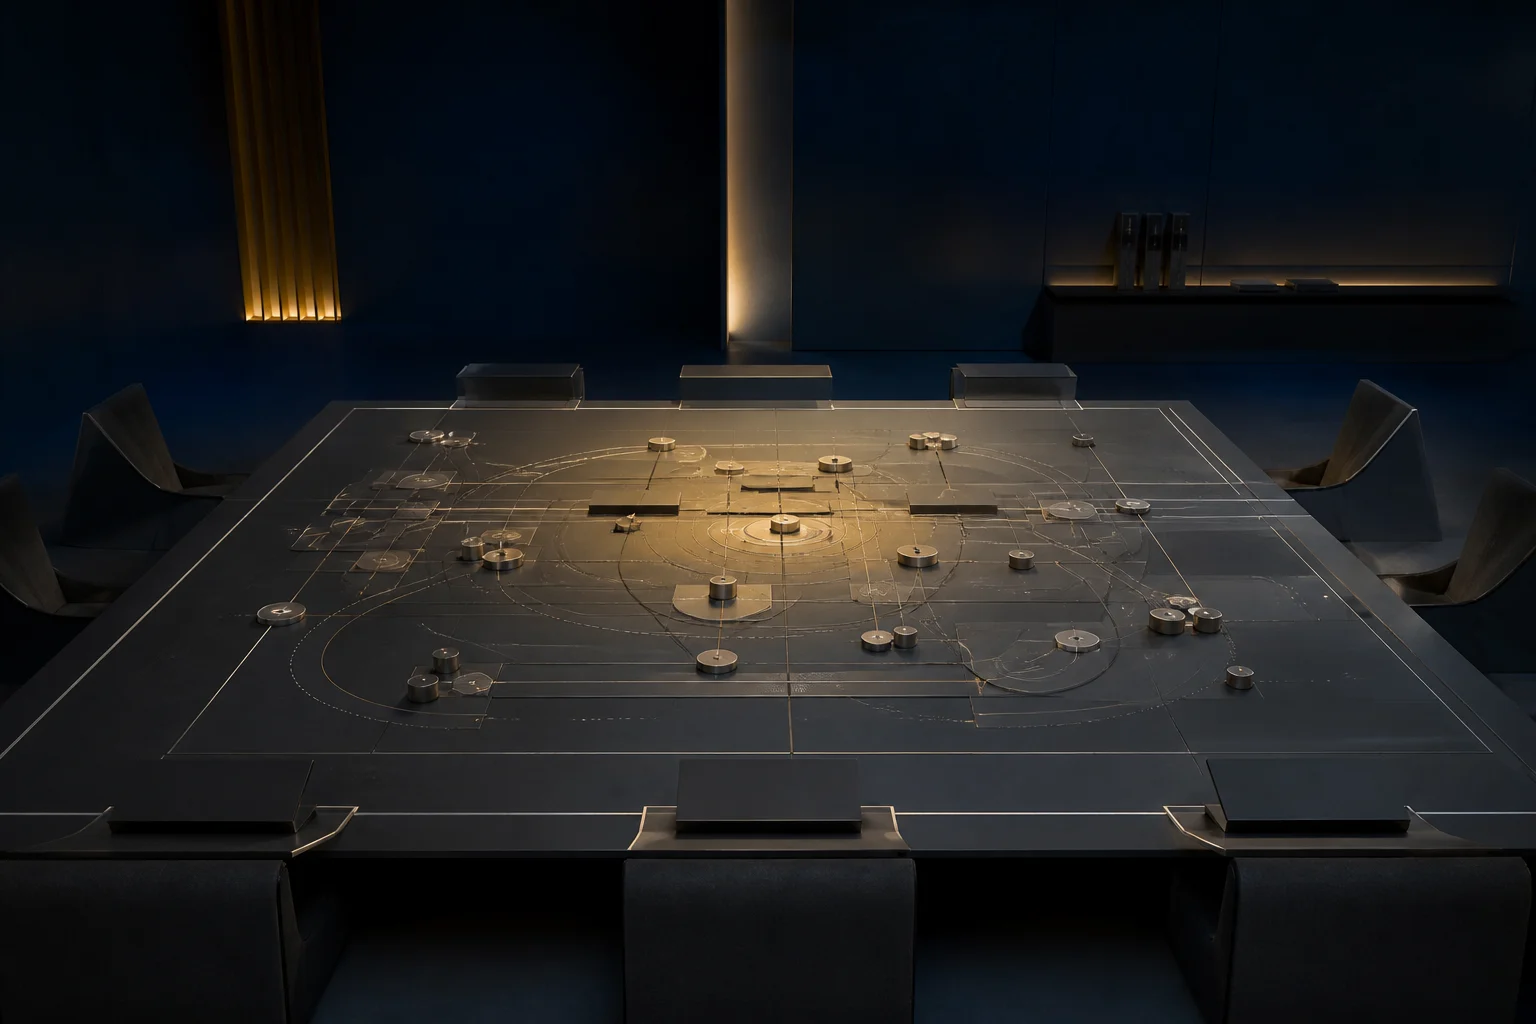
A coordinated scenario table with arranged markers, representing collaborative readiness and tabletop practice

Who it's for

Everyone sees themselves in the platform.

Executives need proof, leaders need one picture, owners need exploitability, and responders need to know the team is ready. The platform answers each.

Executives & boards

The pain

Cannot tell whether cyber risk is actually going down.

What they get

Trend lines, validated findings, and board-ready proof of remediation.

CISOs & security leaders

The pain

Point tools create noise, duplicate records, and unclear priorities.

What they get

One program view across findings, validation evidence, and retests.

AppSec, cloud & IT owners

The pain

Scanner lists do not prove exploitability or business impact.

What they get

Validated exposure with evidence, asset context, and clear remediation status.

Incident response teams

The pain

Exercise notes vanish, and the team trains against last year’s scenario.

What they get

Hands-on range work and custom content aimed at the gaps the team actually has.

Step 01 · Discover

Nothing on your attack surface goes unseen.

The open-source scanner at the core of our visibility layer: continuous discovery, CVE detection, and operator-first triage, free to run anywhere. Sirius Pro is the managed tier: continuous scanning, agent tasking, AI-assisted analysis, and Active Directory auditing, operated by our team at client scale.

  • Continuous asset and attack-surface discovery across network, cloud, and agents
  • Configuration and supply-chain findings, the exposure that CVE-only scanners miss
  • AI-assisted analysis that enriches findings with deployment and threat context
Sirius Security Command Center dashboard

Step 02 · Validate

Proof of what an attacker could actually do.

A continuous penetration-testing environment built on our methodology. It covers more ground between engagements and delivers proven-exploitable findings that our operators review and turn into a remediation roadmap. It runs as a recurring program with an assigned engineer: year-round validation, with human review before any finding is published.

  • Continuous testing across web, cloud, Active Directory, and source code. Our methodology, run year-round
  • Findings are exploited and proven, then adversarially validated to cut false positives
  • Operators review and approve every step. Humans decide what ships, AI is the leverage
Aludra pipeline with a completed validation run, stage logs, and proven findings

Step 03 · See & Act

Your security program, in one place.

The single place clients see engagements, validated exposures, and remediation progress, with the evidence behind every finding and proof that fixes stick. Only findings our operators have reviewed and approved are published, always with clear evidence and source context, and a one-click retest to confirm the fix held.

  • Engagement status, deliverables, and remediation progress in one client view
  • Human-approved, proven-exploitable findings with the evidence and attack-path context behind them
  • Continuous exposure validation programs with recurring runs and one-click retest closure
Open Security Portal shown on a laptop and phone

Step 04 · Improve

Readiness, trained against what you found.

Training closes the gaps each exercise reveals: a hands-on cyber range, a learner content portal, and custom content in one place, so the team gets stronger every cycle.

  • Hands-on cyber range labs in isolated per-student environments
  • Custom scenarios mapped to your architecture and real attack patterns
  • Instructor-led workshops tuned to the roles and gaps on your team
A coordinated scenario table with arranged markers, representing collaborative readiness and tabletop practice

Close the loop with Training.

Train against the gaps in a hands-on cyber range, a learner content portal, and custom content in one place.

Explore Training

See the platform in your environment.

Talk to an operator about where you are in the lifecycle, and the fastest path to proof that your exposure is going down.