Findings without context
Severity scores alone cannot tell you which of 1,200 findings an attacker would actually use first.
This platform, built by Open Security, allows you to see your full attack surface, what changed, and what to prioritize, with operator-first triage that goes beyond a CVE list.
In the hands of an operator, the right tool changes everything.
The Open Security Experience
Vulnerability Scanning is where the Open Security Experience begins: continuous visibility across the attack surface so operators can find what changed, feed validation, and keep the picture current.
The problem
Point-in-time CVE scanning misses configuration drift, supply-chain exposure, and the context that only appears when threat intel meets what is actually deployed. The result: thousands of findings, no exploitability context, and security teams that spend more time exporting CSVs than reducing risk. Organizations do not need more findings. They need better decisions.
Severity scores alone cannot tell you which of 1,200 findings an attacker would actually use first.
Segmented networks and Active Directory need deployed agents and reach, not a scanner running on someone’s laptop.
A raw export is not a risk story. Boards need to see exposure trending down, not a longer list.
How Vulnerability Scanning works
Vulnerability Scanning strengthens Discover in the Open Security Experience, and keeps feeding Validate, See & Act, and Improve as the environment changes.
01 · Discover
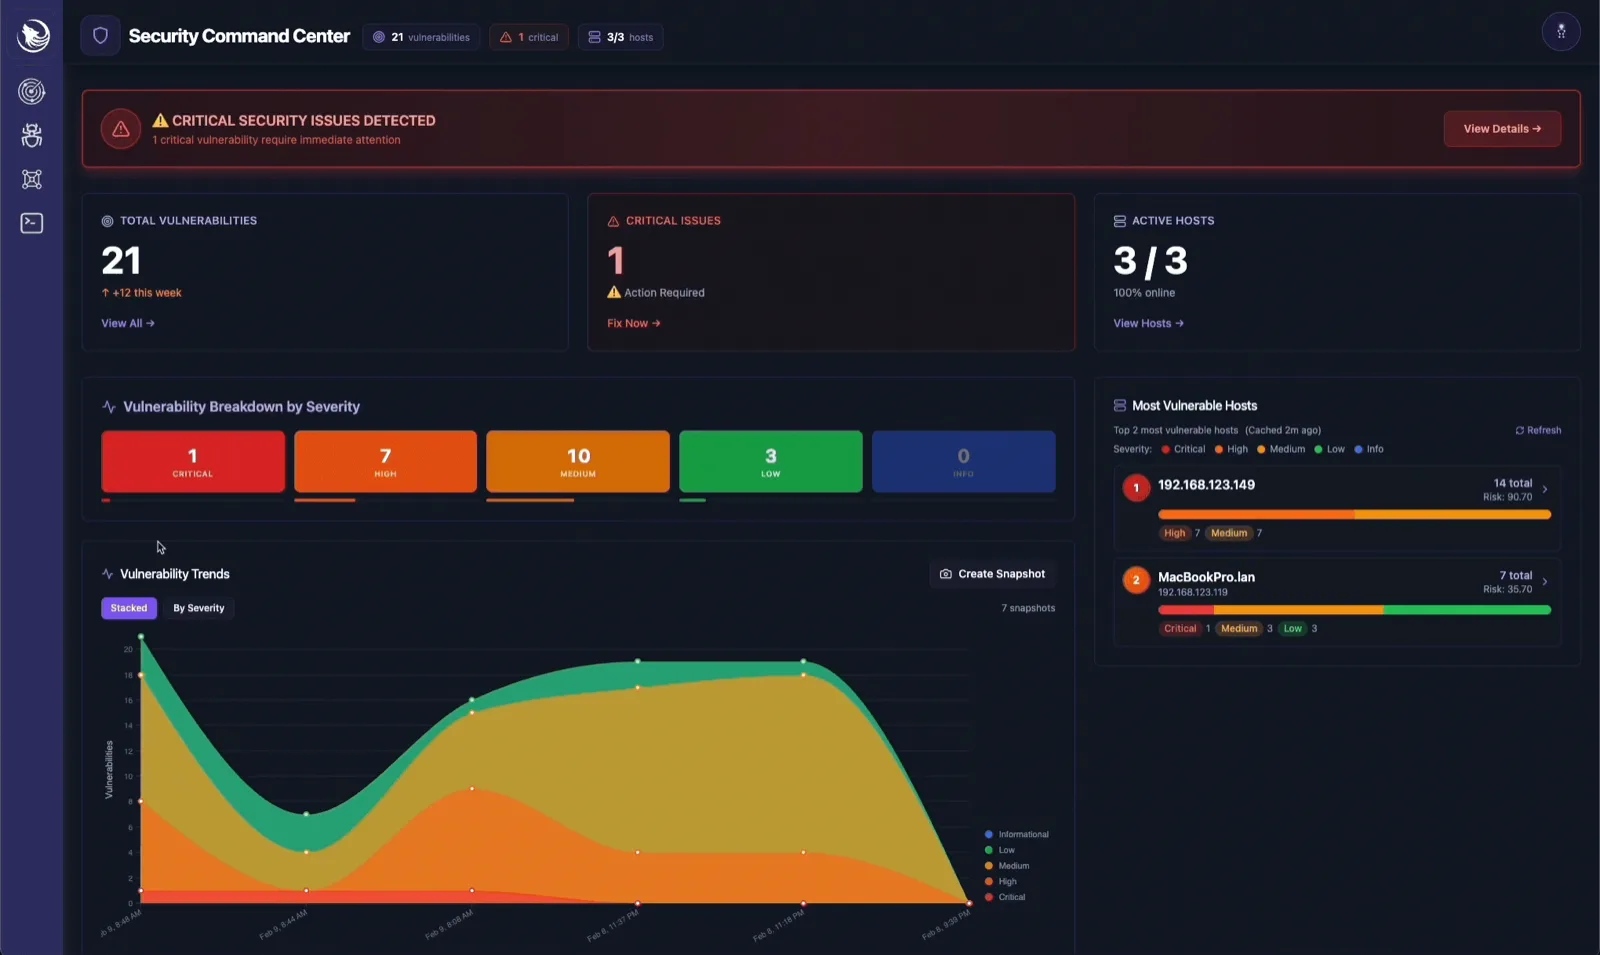
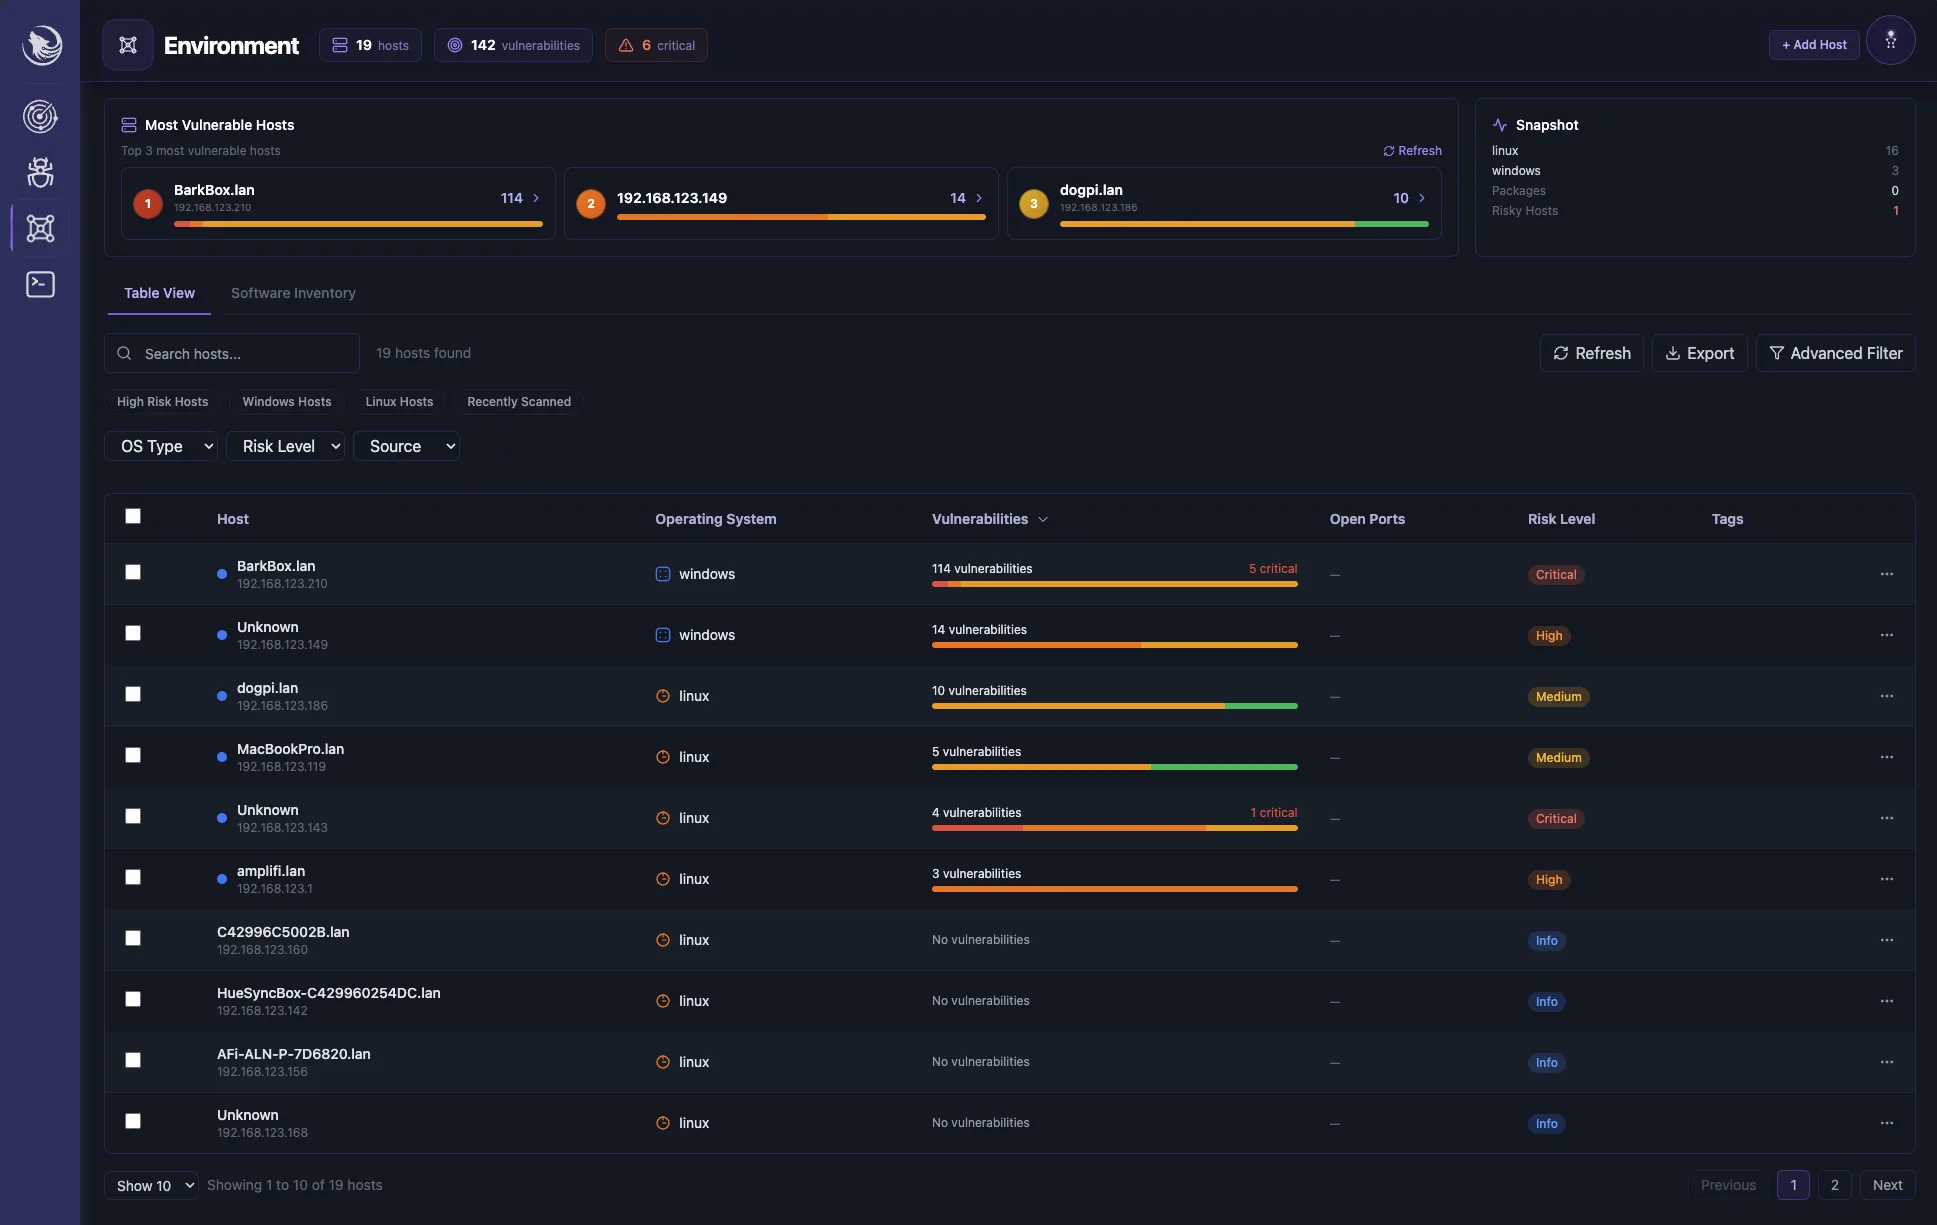
You cannot defend assets you cannot see, and point-in-time scans leave weeks of blindness between snapshots. Vulnerability Scanning unifies network scanning, host-based agent telemetry, and continuous discovery in one live environment view, with deployed agents that reach distributed and segmented networks.
Nothing on your attack surface goes unseen, and new exposure surfaces the day it appears.
02 · Validate
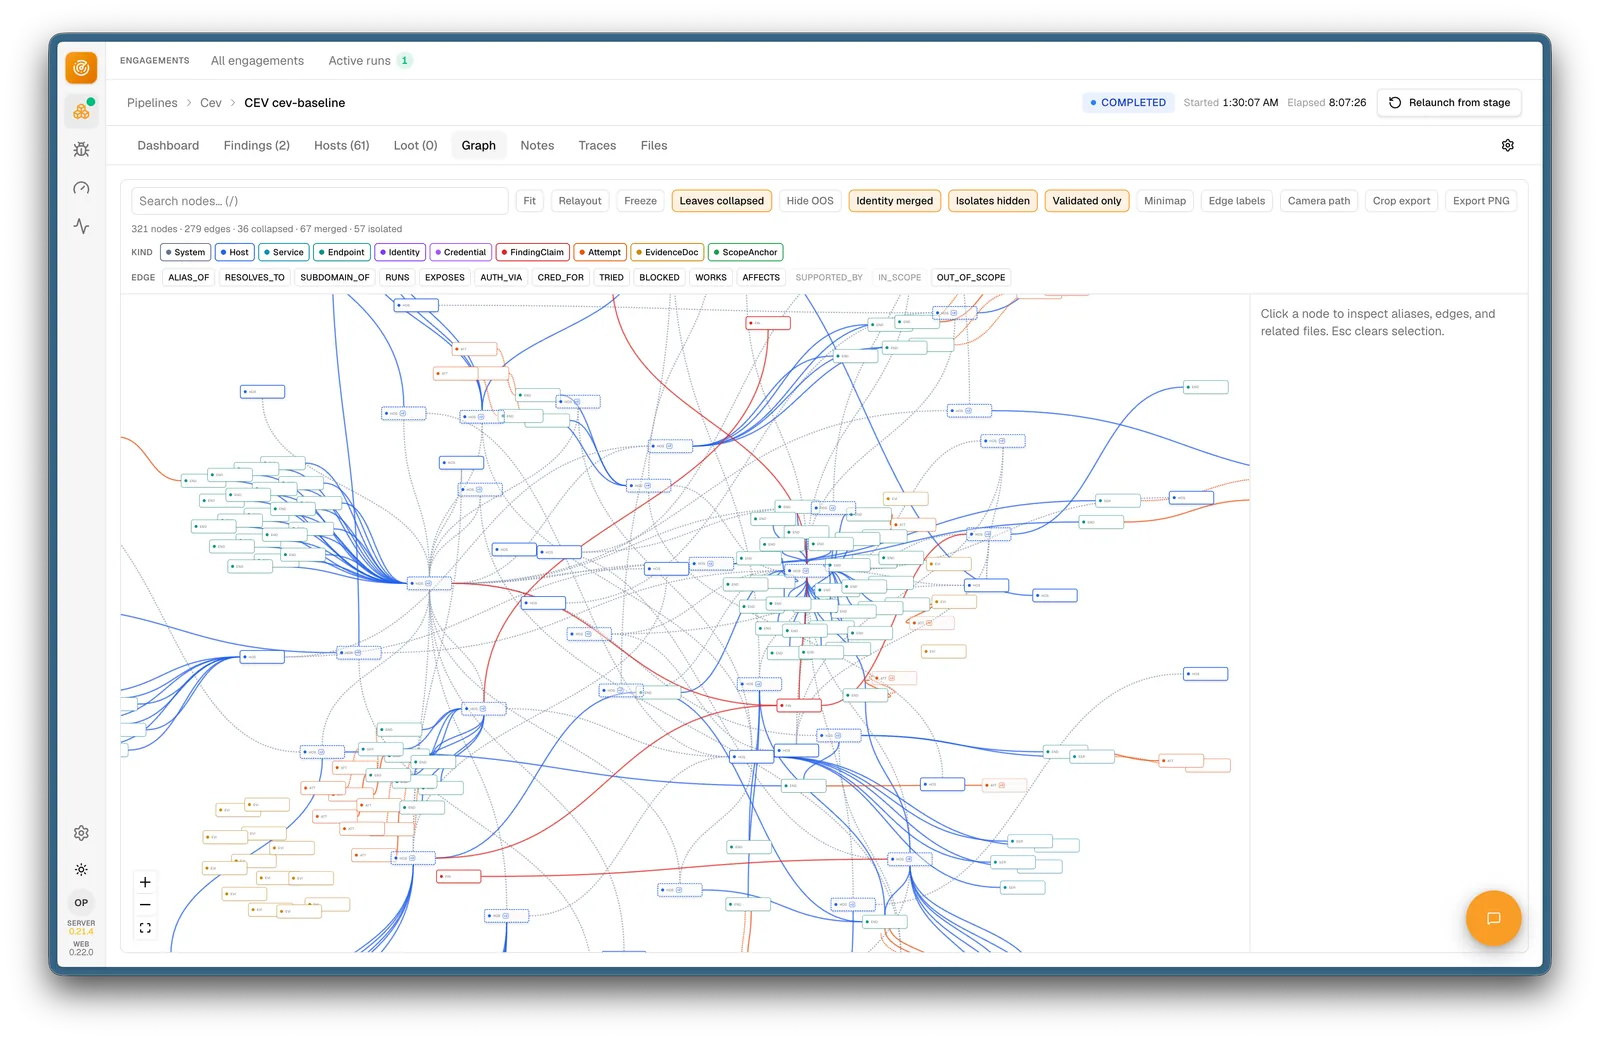
A CVE number and a score do not tell you whether a finding is exploitable in your environment. Vulnerability Scanning adds configuration and supply-chain findings alongside traditional CVE detections, and every finding carries attack-surface context (vector, complexity, privileges, CIA impact, and remediation guidance). Active Directory auditing is driven by Aludra, so exploitable misconfigurations and domain-takeover paths surface for operator validation.
Decisions get made on evidence, not severity colors.
03 · See & Act
AI-assisted analysis adds deployment context and threat intelligence to every finding, so your team gets a clear, ranked queue of the work that reduces risk most.
Your team stops burning hours on theoretical noise.
04 · Improve
The Aludra platform turns live exposure into the view leadership needs, with vulnerability trends, severity breakdowns, and risk scoring that track your posture quarter to quarter. Findings flow into Aludra Vulnerability Management, so you can show measurable progress over time.
Measurable exposure reduction you can take to the board.
Continuous visibility, in view
When you need it
Vulnerability Scanning is the lowest-friction way to start seeing your attack surface the way operators do, without buying the entire platform first.
Thousands of findings, no exploitability context, and a team that spends more time exporting CSVs than reducing risk.
You do not need more findings. You need better decisions.
Point-in-time snapshots go stale the day after they run. New hosts, ports, and packages appear in the gap.
See exposure the day it appears, not at the next quarterly scan.
A raw export is not a risk story. Boards need exposure trending, not a longer list.
Walk in with proof, not another spreadsheet.
Triage, investigation, and remediation live in different tools, so the people doing the work lose hours to swivel-chairing.
One operator-first interface. Built by people who use it.
Human in the loop
Vulnerability Scanning automates discovery, inventory, and ranking so operators spend time on judgment: which findings matter, which to fund, and which to defer. The tool does not replace the operator. It was built by them.
Technology creates leverage. Operators create confidence.
Vulnerability Scanning
Open Security operators
Decisions you can defend
Operator-built
Our scanner wasn’t designed by a product committee. It was built by practitioners with military and cyber warfare backgrounds who live in these workflows every day. They built the scanner they needed.
Built for the engineer doing the work, not a product committee’s idea of a scanner.
Live agent operations and command execution, not a read-only portal.
Configuration and supply-chain exposure sit alongside traditional detections.
The same interface that powers Open Security assessments every day.
Built by former military and cyber warfare operators who know what attackers look for.
Domain-takeover paths are mapped by the validation environment, not a signature scan.
Close the loop
Vulnerability Scanning keeps the attack surface current so validation, remediation, and readiness have something true to work from. What you find here becomes more powerful when Aludra proves it and Portal tracks the fix.
The Open Security Experience
Talk to an operator about Vulnerability Scanning: continuous scanning, configuration and supply-chain findings, AI-assisted analysis, and Active Directory auditing. Pair it with Aludra and our operators prove which of those exposures are actually exploitable.